This behavior has been introduced since Elements Connect 8.0.2.
Symptoms
-
A URL/REST API datasource that previously worked now fails and the following error appears:
"The access to the URL is forbidden because it is not allowed on this server." -
Typically affects URLs pointing to
localhost,127.0.0.1, or internal/private hosts (for example10.x.x.x,172.16–31.x.x,192.168.x.x), as well as IPv6 loopback/link-local/unique-local addresses.
Cause
To prevent server-side request forgery (SSRF), Elements Connect now blocks datasource requests that resolve to loopback, link-local, site-local (private), any-local, multicast, or IPv6 unique-local addresses.
How to check if you are affected
-
Look at the host in the datasource URL (obvious cases are
localhost,127.0.0.1, or0.0.0.0). -
For a named host, resolve it to its IP address directly from the Jira server, using the following commands (the resolved address is what matters, not the hostname):
-
Linux/macOS:
nslookup your-host.example.comordig +short your-host.example.com -
Windows:
nslookup your-host.example.com
-
-
Compare the resolved IP against the following address ranges:
-
127.0.0.0/8(loopback) -
10.0.0.0/8,172.16.0.0/12,192.168.0.0/16(private) -
169.254.0.0/16(link-local) -
0.0.0.0(any-local) and multicast (224.0.0.0/4) -
IPv6:
::1,fe80::/10,fc00::/7
-
-
If the resolved IP matches any of these ranges, the datasource is affected.
A quick way to confirm that the IP address is what is causing the issue: if the same data can be reached using a public hostname that resolves to a public IP address, that version will work correctly while the internal one is blocked.
Example
The nslookup command resolves to the following internal IP address: 192.168.10.2
This address belongs to the 192.168.0.0/16 network referenced in the list above.
This address is therefore blocked.
Resolution
-
If the data is truly external, it must be exposed through a public hostname or HTTPS endpoint that is independent of the Jira Data Center server. The datasource URL must then be updated accordingly.
-
If you are querying your own Jira instance, upgrade to 8.0.4 or later, where requests to your own Jira host are explicitly allowed again.
-
If you want to query an internal service behind your proxy then you have to add the URLs to the allowlist (see below)
How to allow an internal URL
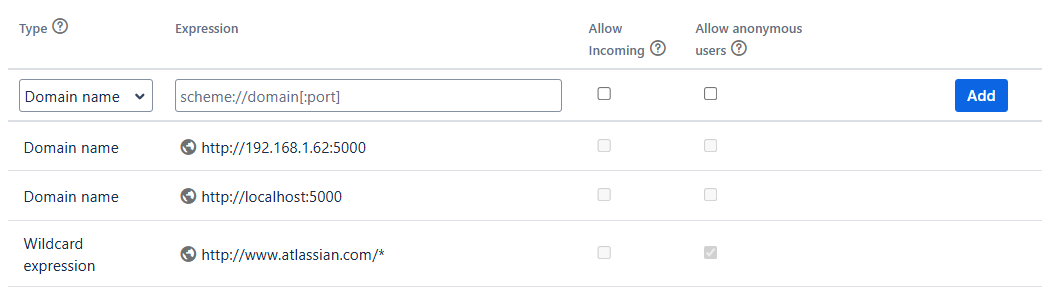
If the internal service is one you trust and intend to use, you can add it to the Jira's Allowlist feature:
-
Go to Administration → System → Security → Allowlist.
-
Add an entry that matches your datasource URL / IP address (Jira supports exact, wildcard, and other rules)
-
Save the entry.
-
Re-test the URL / IP address in Elements Connact
Once the URL / IP address matches an allowlist entry, Connect treats it as administrator-approved and permits it even though it resolves to a private/internal address. This is a deliberate, admin-controlled decision: only URLs you have explicitly added are allowed.
What is never allowed — even via the allowlist
For safety, cloud provider metadata endpoints are always blocked, regardless of the allowlist. These endpoints can expose instance credentials and are never a legitimate data source:
-
169.254.169.254— AWS, Google Cloud, Azure, OpenStack, DigitalOcean metadata service -
100.100.100.200— Alibaba Cloud metadata service -
fd00:ec2::254— AWS metadata service over IPv6
Adding any of these to the Jira allowlist will not make them reachable from a Connect data source.